




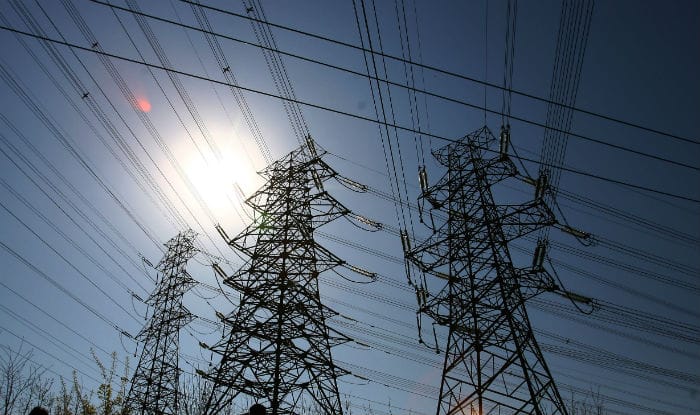
Hyderabad: Days after a report of the China-based cyber-attack during last year’s power outage in Mumbai, the Computer Emergency Response Team of India (CERT-In) issued an alert that helped avert a similar hacking attempt of the power systems at Telangana’s TS Transco and TS Genco allegedly by the same Chinese group. TS Transco and TS Genco run the power utilities in the state.
The China-based malware targeted at least 40 substations in Telangana, The Times of India quoted a trusted source of the CERT-In, but the attack was successfully thwarted by the state government agencies. According to the report, the China-based groups were trying to communicate with TSLDC systems and take control of the server.
The hackers were reportedly attempting to steal data and disrupt the power supply in the state. GENCO subsequently blocked the suspected IP addresses and changed the user credentials of all officials operating remotely as a precautionary measure.
“China-based threat actor group command and control servers were trying to communicate with systems belonging to Telangana SLDC (State Load Dispatch Centre). We have directed the state power utilities to take all protection and safety measures,” noted Telangana Transco and Genco chairman and managing director D Prabhakar Rao.
The Telangana cyber-attack attempt assumes special significance in light of a US-based report that the 2020 Mumbai blackout was caused by a China-based cyber-attack.
On October 12, a grid failure in Mumbai resulted in a massive power outage, stopping trains on tracks, hampering those working from home amidst the COVID-19 pandemic and hitting the economic activity hard.


For breaking news and live news updates, like us on Facebook or follow us on Twitter and Instagram. Read more on Latest India News on India.com.
